
Energy
Access with approval, without the queue
An energy company sends every access change past the approval that belongs with it, and then carries it out automatically. The care stayed, the waiting went.
- employees under management
- 200employees under management
- changes a month, handled automatically
- around 25changes a month, handled automatically
- with the approval that belongs to it
- Every stepwith the approval that belongs to it
Careful, but slow, and the evidence was everywhere and nowhere
In the energy sector access is not granted lightly. Many permissions need sign-off from a manager or from the owner of the system, and that sign-off has to be findable later. That comes with a sector where the wrong access has real consequences.
At this company, with around two hundred employees, those approvals ran outside the access process. A request went by email to whoever had to approve it, the approval came back by email, and then someone still had to carry it out by hand. The process was careful as a result, but slow, and the evidence that it had been careful was scattered across mailboxes and tickets.
What they wanted: the approval inside the process, not beside it
The company wanted to keep the care and lose the waiting. That is only possible if the approval is part of the access request itself: request, sign-off and execution as one chain, where the next step only begins once the previous one is done, and where it is visible afterwards who approved what and when.
And the standard cases, the onboarding, role changes and offboarding that are simply fixed for every role, should need no request at all. Only what deviates from the standard belongs in front of an approver.
An approval should not slow the process down. It should sit inside it.
What was built: request, sign-off and execution as one chain
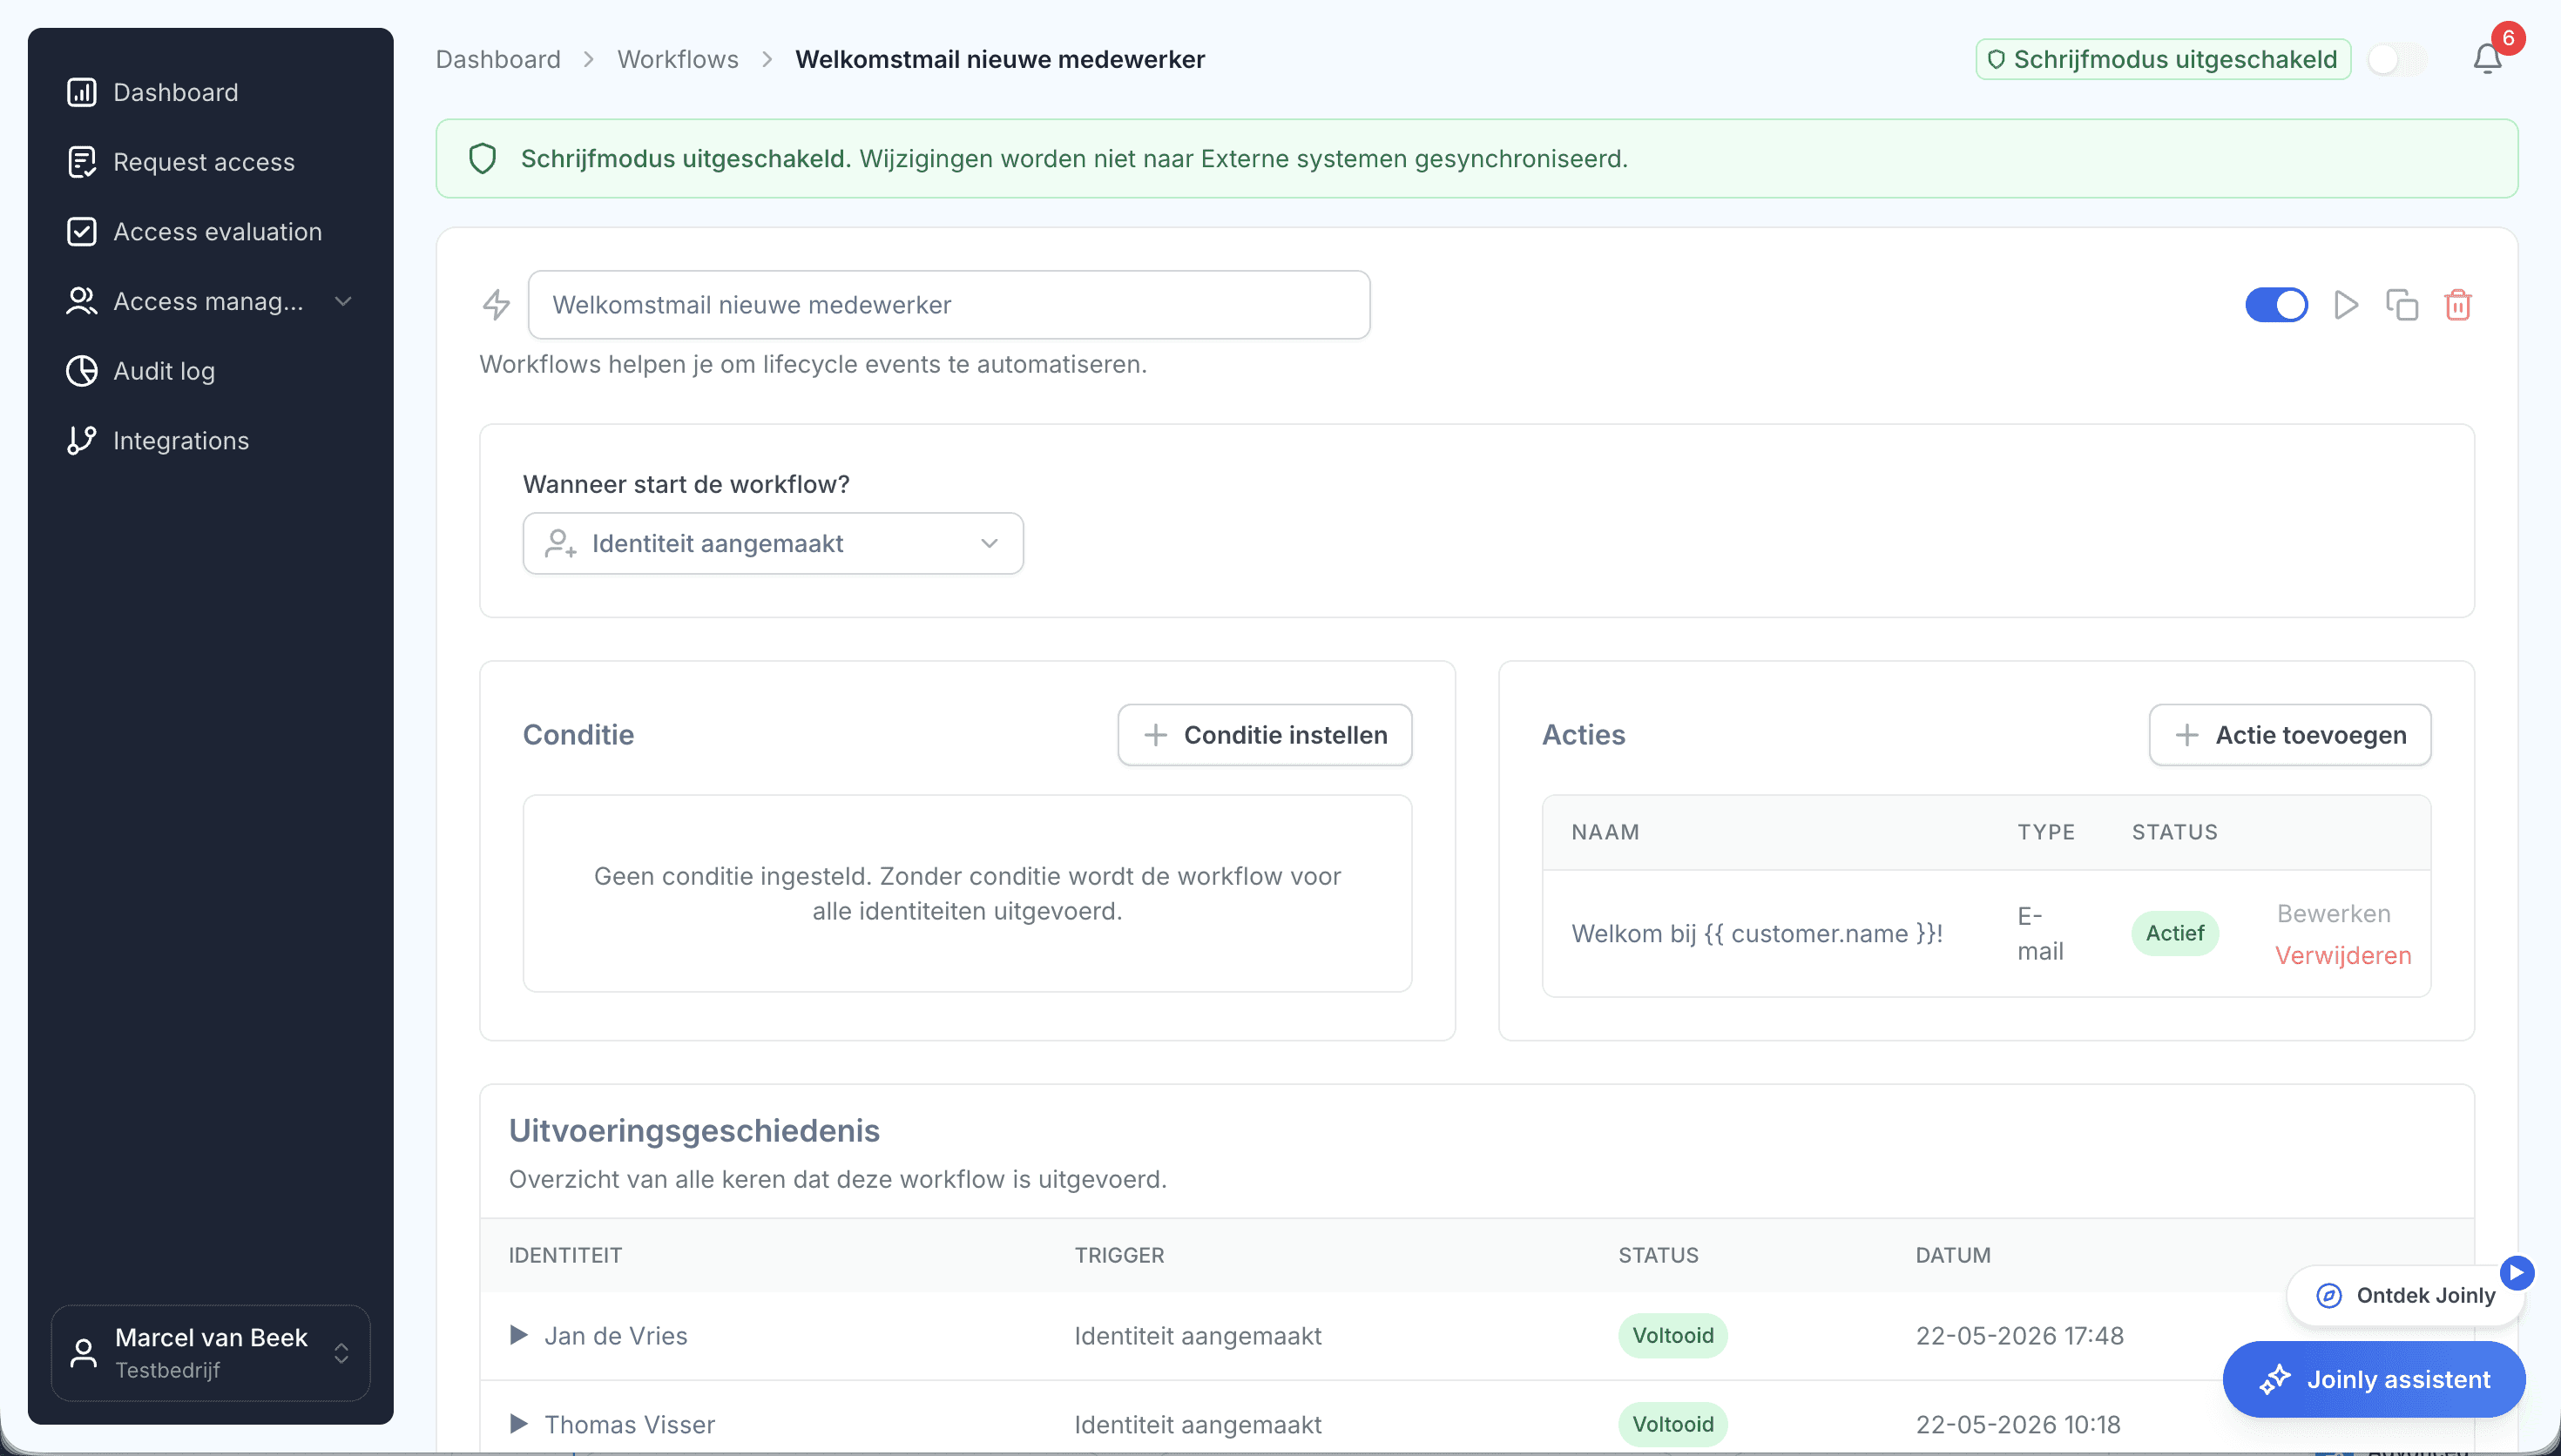
An access request goes from Joinly to the company's ITSM system as an approval. What is approved, Joinly carries out; what is not approved does not happen. The sign-off sits with the request, and the execution sits with the sign-off.
From the approved request follow the groups in Active Directory. And the standard cases run from HR without a request: what belongs to the role is ready on the first day, and when someone leaves it goes away again on the last.
Today: careful and fast, with the evidence in one place
The approval stays where it belongs. The waiting between the steps is gone, and so is carrying it out afterwards. Every access change used to be an email exchange, a sign-off and a manual adjustment. Now it is one chain that finishes itself.
Who requested it, who approved it and what happened next now sit together. At an audit that is the answer, and it is ready before the question is asked.
What you can count on
- No vendor lock-inYour identities and your configuration stay yours.
- Your data out whenever you wantYou can export your data at any time.
- Standard SLAOur standard SLA is available on request.
- Support during implementationOur specialists set it up together with you.
- ISO 27001 certifiedInformation security to an internationally recognised standard.
Customer stories
More customer stories
Organisations with a similar question, in a different sector.
Public sector
Access that follows the job, in an organisation that accounts for itself
more than 600 employees
Read the story
Aviation
The basis in order, in a sector where everything has to be demonstrable
more than 1,000 employees
Read the story
Utilities
Its own Active Directory, following the HR records by itself
200 employees under management
Read the story
Want to see what this means for your organisation?
Book a 30-minute demo. We walk through your own situation: which HR system you use, which systems need to follow and what can be automated first.
Book a demo