
SAP Successfactors → AD On premise
Connect SAP SuccessFactors to Active Directory (on-premise)
When someone joins, moves or leaves in SAP SuccessFactors, you want that change reflected in your on-premise Active Directory without anyone touching it by hand. To connect SAP SuccessFactors to Active Directory, Joinly reads each HR change in Employee Central through the OData API and applies it to your domain through the Joinly AD Agent — a lightweight connector that runs inside your network. SuccessFactors stays your source of truth; Joinly is the engine that keeps every account in the right OU, accurate and traceable.
Key takeaways
Employee Central stays your source of truth; Joinly applies every joiner, mover and leaver to on-premise Active Directory automatically.
The Joinly AD Agent runs inside your network and needs only an outbound HTTPS connection — no inbound ports and no domain controller exposed to the internet.
Joinly maps SuccessFactors foundation objects to the right AD security groups and target OUs, and builds the sAMAccountName, UPN and distinguished name from your own rules.
Reads effective-dated records and resolves concurrent employment, so accounts land in the correct OU on the start date and aren't broken by a second assignment.
Every action is logged for a complete audit trail, aligned with NIS2 and ISO 27001 — and the same setup extends to a hybrid Entra ID environment.
Quick facts
Source system | SAP SuccessFactors (Employee Central) |
Target system | On-premise Active Directory (AD DS) |
Connection method | Employee Central OData API → Joinly AD Agent → Active Directory |
Agent requirement | Domain-joined Windows server, outbound HTTPS (443) only |
Supported events | Joiner, mover, leaver (incl. rehire, worker conversion, concurrent employment) |
Synced attributes | Name, sAMAccountName, UPN, mail, department, job title, manager, cost center, distinguished name / OU, start and end date |
Real-time or batch | Frequent sync, multiple times per day |
Compliance | ISO 27001, NIS2-ready, GDPR (EU data centre) |
Liever in het Nederlands? SAP SuccessFactors koppelen met Active Directory (on-premise)
How does Joinly sync SAP SuccessFactors to Active Directory?
Joinly reads each HR change in Employee Central in the cloud, then hands the action to the Joinly AD Agent inside your network, which makes the change in Active Directory. Employee Central holds the authoritative employment record; the agent is the only component that touches your domain.
Joiner. HR completes the hire in Employee Central. Joinly reads the new records, determines the role from department, job classification and cost center, and instructs the AD Agent to create the user in the correct OU, build the sAMAccountName and UPN from your rules, and add the right security groups — timed to the effective start date.
Mover. When someone changes position, department or legal entity, Joinly tells the agent to move the user to the matching OU, swap security-group membership and update attributes. Access that no longer fits the new position is removed, so permissions stay aligned with the actual job.
Leaver. On the termination date, Joinly instructs the agent to disable the AD account and optionally move it to a disabled-users OU. Concurrent employments are taken into account, so an account is only disabled when the last active employment ends.
Example: A logistics company runs Employee Central and an on-premise AD across three sites. It hires a warehouse planner with a start date next Monday. Joinly reads the effective-dated record, and on Monday morning the AD Agent creates the user in the Site-A > Operations OU, sets the sAMAccountName to a unique pattern, and adds the Warehouse-Operations group. When the planner later moves to dispatch, the agent moves the object to the new OU and swaps the groups the same day.
What manual AD account management costs
Without automation, every account starts as a SuccessFactors ticket that an admin works through in Active Directory Users and Computers by hand — creating the object, choosing the OU, building the sAMAccountName, adding groups. Microsoft's Entra provisioning agent can push SuccessFactors data to on-premise AD, but it offers limited mapping, no role-to-group logic and the same effective-dating and concurrent-employment gaps, so the decisions still fall to people.
Onboarding delays. New joiners wait for an AD account and group access while a ticket sits in a queue, losing productive days in their first week.
Permissions that don't keep up (privilege creep). When movers change position, old security-group membership often stays attached, so people accumulate rights they no longer need.
Forgotten offboarding. Accounts that aren't disabled on time are a security and audit risk — and with concurrent employment it is easy to disable an account while another employment is still active.
Joinly vs. the Entra provisioning agent for AD
Microsoft's Entra provisioning agent can write SuccessFactors data to on-premise AD, but it stops short of the part that actually decides access. Here's how the two compare for an Employee Central-driven AD setup.
Joinly AD Agent | Entra provisioning agent (SF → AD) | |
|---|---|---|
Source | Reads Employee Central OData directly | Reads SuccessFactors directly |
OU placement | Rule-based on foundation objects | Single configured container; limited logic |
Role-to-group mapping | Built in, rule-based | Not available out of the box; manual |
Effective-dated / future hires | Times creation to the effective start date | Needs custom date-window configuration |
Concurrent employment | Resolves home vs host employment | Known pitfall; wrong employment can sync |
sAMAccountName / UPN rules | Custom transformation with uniqueness fallback | Limited expression mapping |
Audit trail | Per-action logging tied to the HR source | Limited |
Watch-outs when connecting SAP SuccessFactors to Active Directory
A few details decide whether this connection stays reliable at scale.
sAMAccountName uniqueness and length. AD limits the sAMAccountName to 20 characters and it must be unique across the domain. Joinly builds it from your rules with a fallback pattern, so duplicate names never produce a collision or a truncated, unreadable login.
OU placement from foundation objects. Legal entity, business unit, division and department don't map one-to-one to your OU structure. Joinly builds explicit rules that place each user — and move them on a transfer — into the correct OU.
Effective-dated future hires. Employee Central stores a hire as a future-dated record before the first working day. Joinly reads the effective start date and has the agent create the account on the right day, not before.
Concurrent employment. An employee can hold more than one active employment. Joinly applies rules to keep a single, stable AD object driven by the home employment, so a second assignment adds groups rather than creating a duplicate account.
Service-account permissions. The agent acts under a service account with delegated rights. Joinly works with least-privilege delegation scoped to the target OUs, so the agent can create, move and disable users without domain-admin rights.
Joinly handles each of these by default with custom mapping and transformation.
Always audit-ready
Every account action the Joinly AD Agent performs is logged in the Joinly cloud: who was affected, when it happened, which OU and groups changed and which SuccessFactors change triggered it. For NIS2 that matters directly: access can be traced back to an authorised HR source rather than an ad-hoc request. Joinly is ISO 27001 certified, runs in an EU data centre in Amsterdam, applies least-privilege by default, and is built to meet NIS2 and ISO 27001.
Example case
A regional healthcare provider with around 2,400 employees across twelve locations ran Employee Central but still lived in an on-premise Active Directory for its clinical systems. Every new nurse, doctor or support worker started as a SuccessFactors ticket that IT processed by hand in AD — creating the object, choosing the OU, building the login, adding groups. With seasonal contracts and frequent internal transfers the queue never emptied, and new joiners regularly waited until day two or three for their account.
After connecting SAP SuccessFactors to Active Directory with Joinly, that work disappeared. The Joinly AD Agent now creates each user in the right OU on the start date, builds a unique sAMAccountName, adds the correct security groups, moves people on a transfer and disables accounts on the termination date with a 30-day grace window — all driven by the HR change in Employee Central.
"An account is simply ready in the right OU when the nurse walks in, transfers move themselves, and we can show the auditor exactly which SuccessFactors change created every bit of access." (Head of IT at a regional healthcare provider)
The result: onboarding time dropped from days to zero touch, privilege creep from old roles was eliminated, and the team walked into its last NIS2 assessment with a complete, source-backed audit trail.
Installation guide
Follow these steps to connect SAP SuccessFactors to your on-premise Active Directory with Joinly. Most of the setup happens in the cloud platform; the only local component is the lightweight Joinly AD Agent, which you install on a domain-joined server.
1. Create your account
Go to platform.joinly.app and create your account.
Note: charges may apply for using the platform after the trial period ends.
Sign up at platform.joinly.app to get started.
2. Find the SuccessFactors integration in the Joinly marketplace
Open the Joinly marketplace and search for the SAP SuccessFactors integration.
Don't see your system listed? Get in touch at support@koppelhet.nl and we'll help you out.
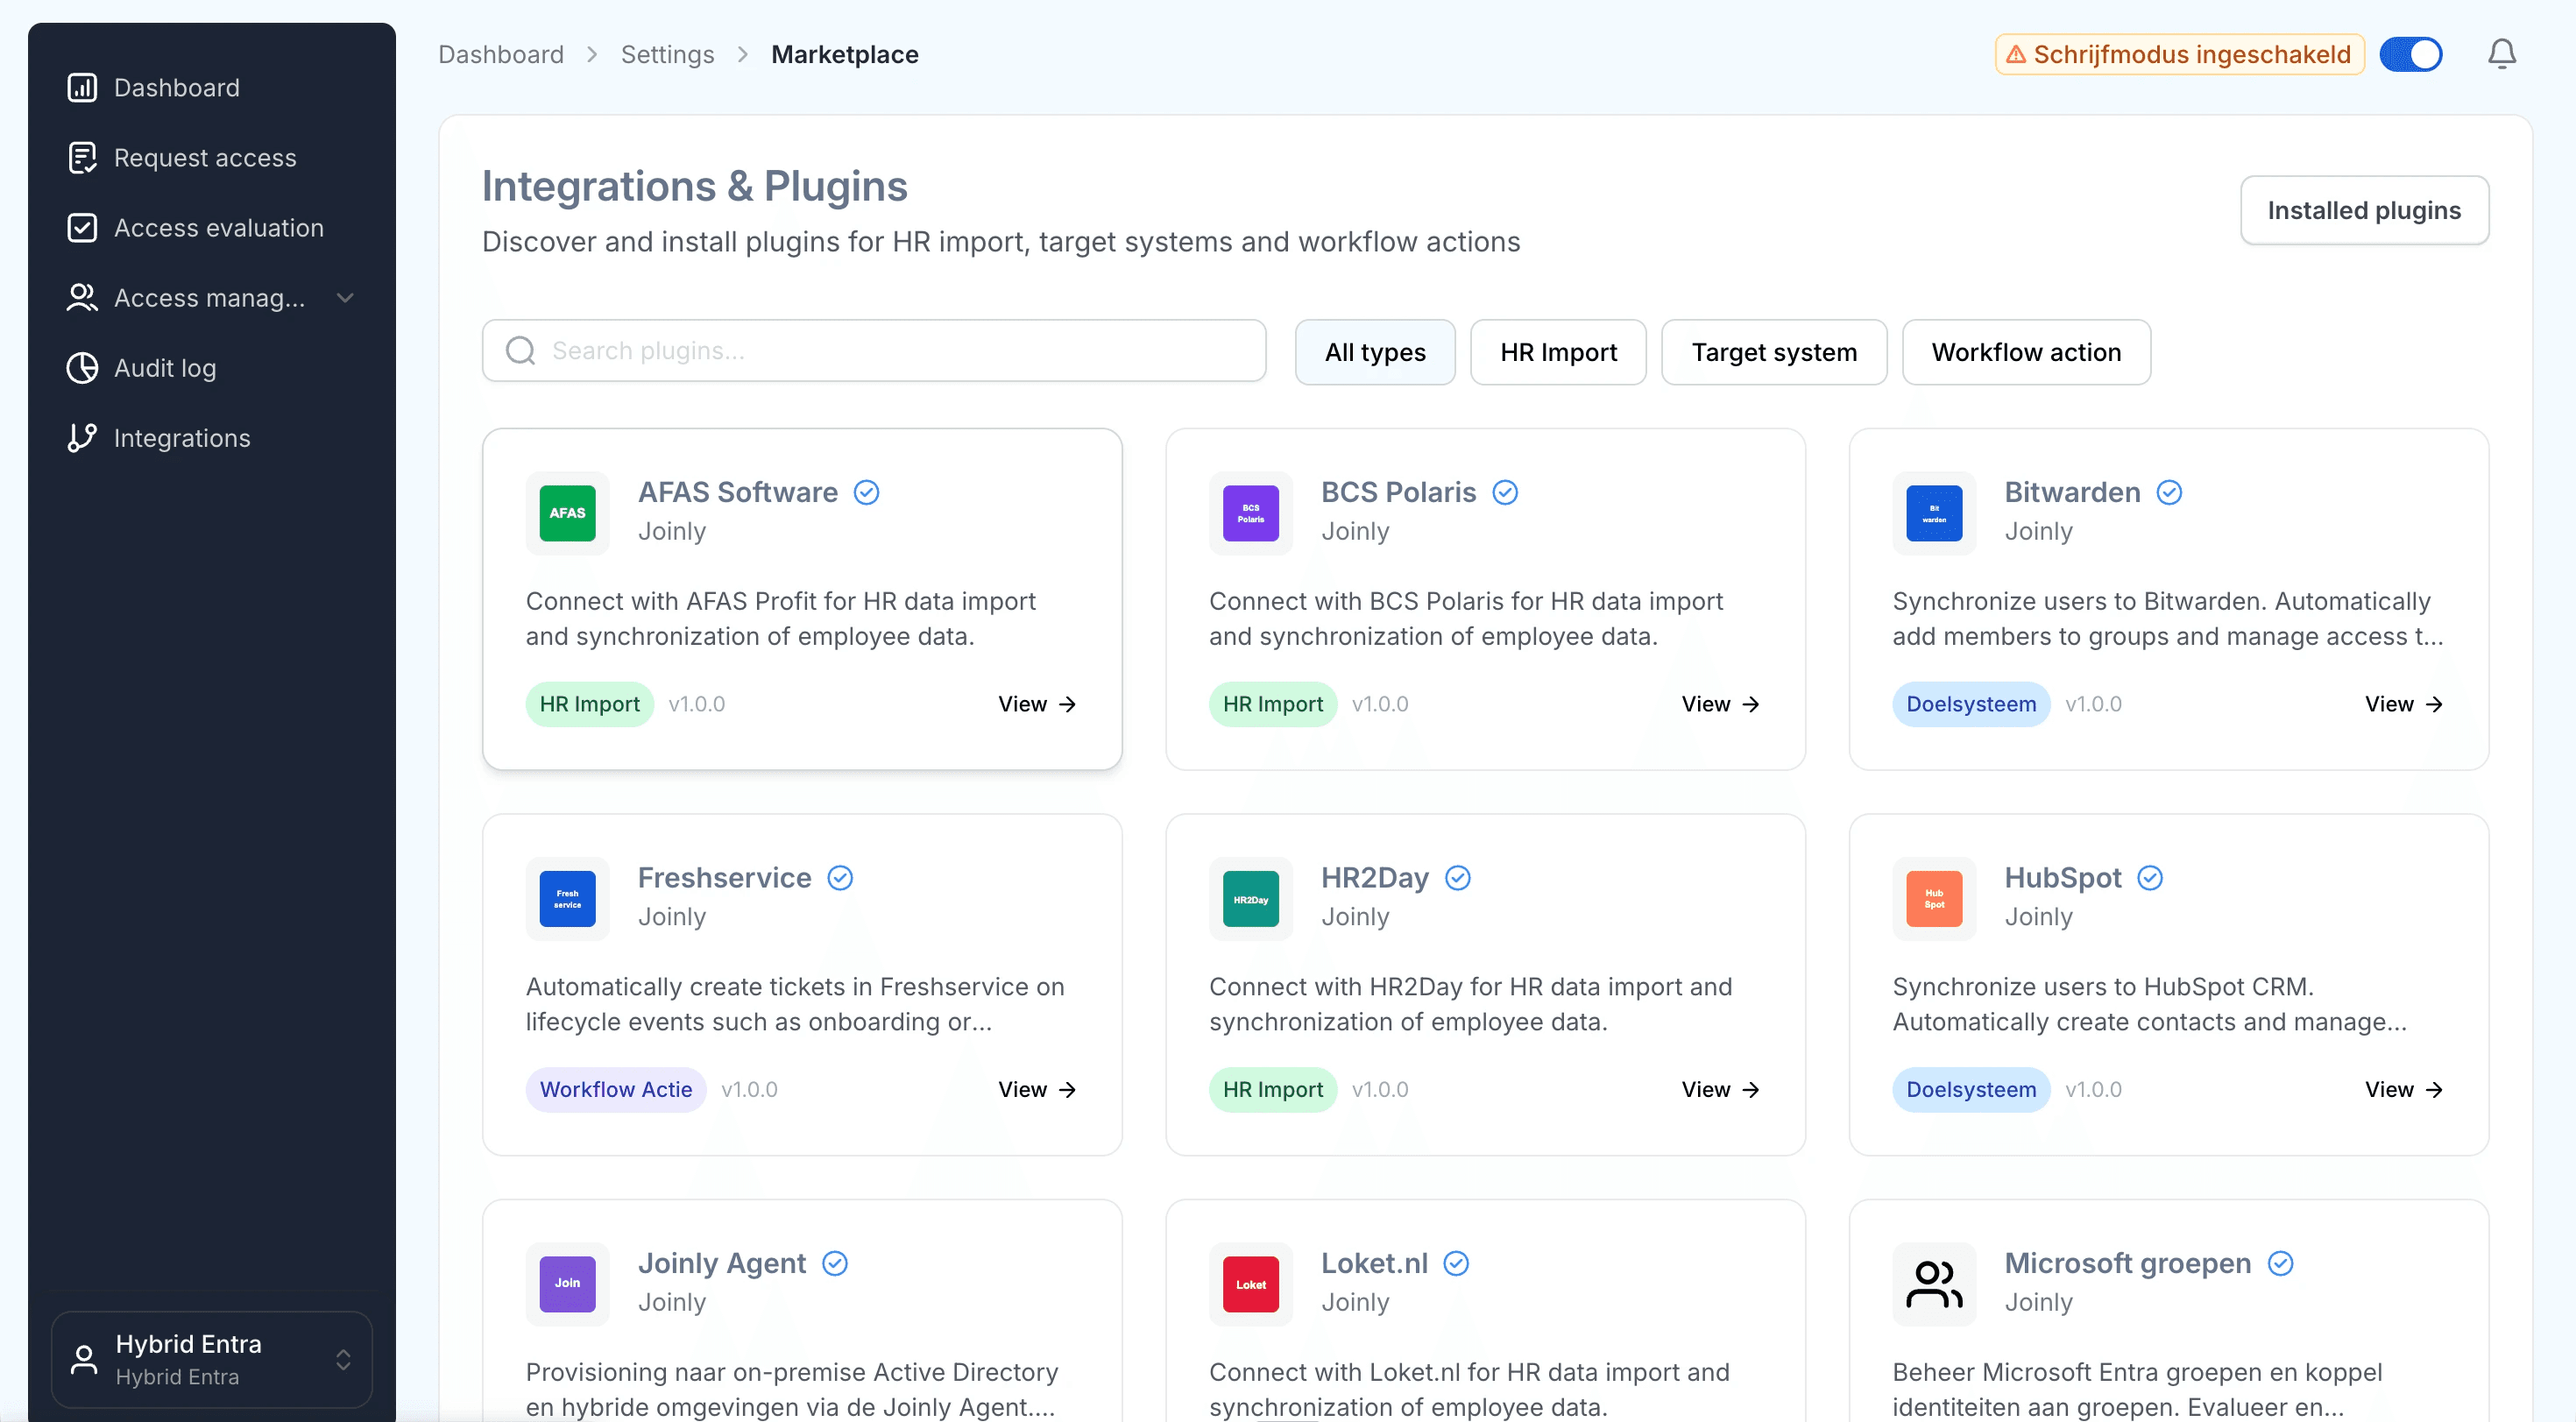
Search the marketplace for the SAP SuccessFactors integration.
3. Follow the installation wizard
You may be redirected to integrations.joinly.app. Create an account there and enter your SuccessFactors connection details: your API server URL, company ID, and OAuth credentials (SAML Bearer Assertion or X.509). All data is encrypted and stored securely.
Enter your SuccessFactors API endpoint, company ID and OAuth credentials in the wizard.
4. Download the Joinly AD Agent
In the platform, go to Workflows -> Select a workflow -> Add action -> Select 'Provisioning via Agent' and download the installer. The agent is a lightweight Windows service that connects your domain to the Joinly cloud over an outbound HTTPS connection only — there are no inbound ports to open.
Read the full Joinly AD Agent installation guide here.
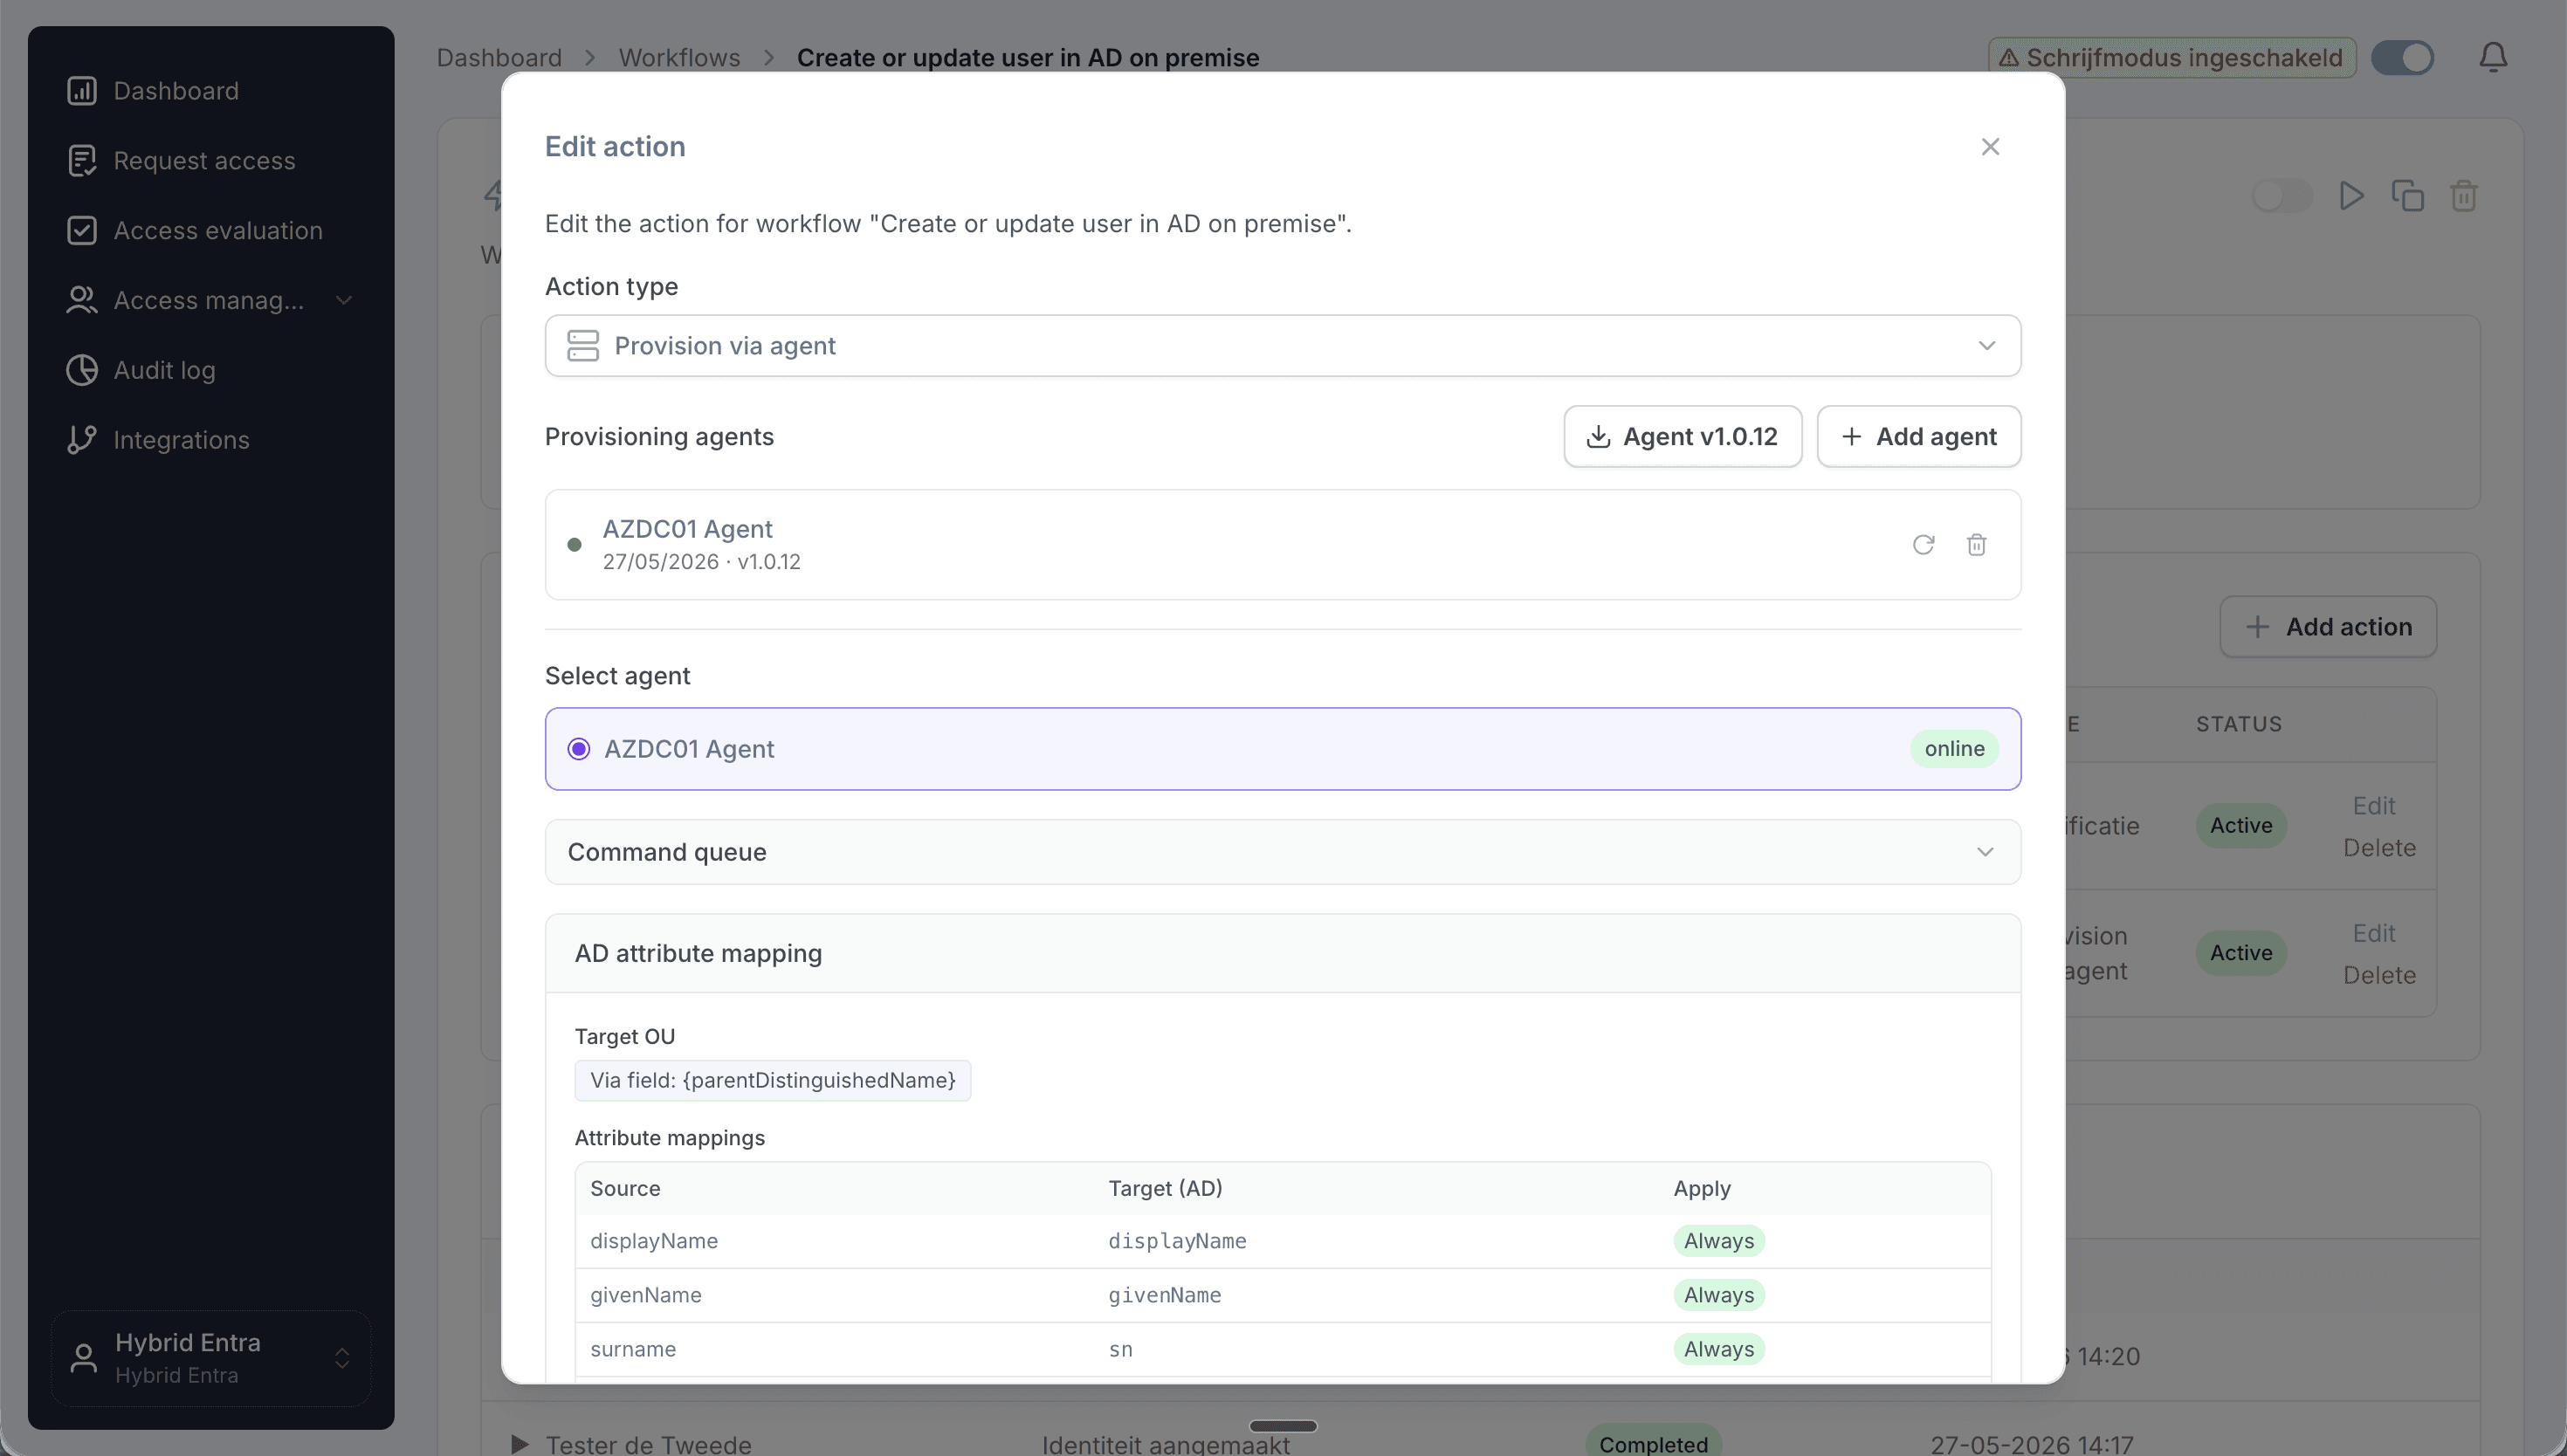
Download the Joinly AD Agent installer from the provisioning settings.
5. Install the agent on a domain-joined server
Run the installer on a domain-joined Windows server that can reach a domain controller. The server needs outbound HTTPS (port 443) to the Joinly cloud and a GMSA account installation on your domain controller. Run through the installer; it registers the agent as a Windows service that starts automatically.
6. Pair the agent with your Joinly tenant
Copy the pairing token from Settings → Provisioning → AD Agent in the platform and paste it into the agent's configuration screen. The agent uses the token to register securely with your tenant; once paired, its status shows as Connected in the platform.
Pair the agent with your tenant using the pairing token.
7. Set the target OU and attribute mapping
Configure where users are created and how their attributes are built. Map the distinguished name / OU from foundation objects, and build the sAMAccountName, userPrincipalName, mail, department and manager with Liquid templates.
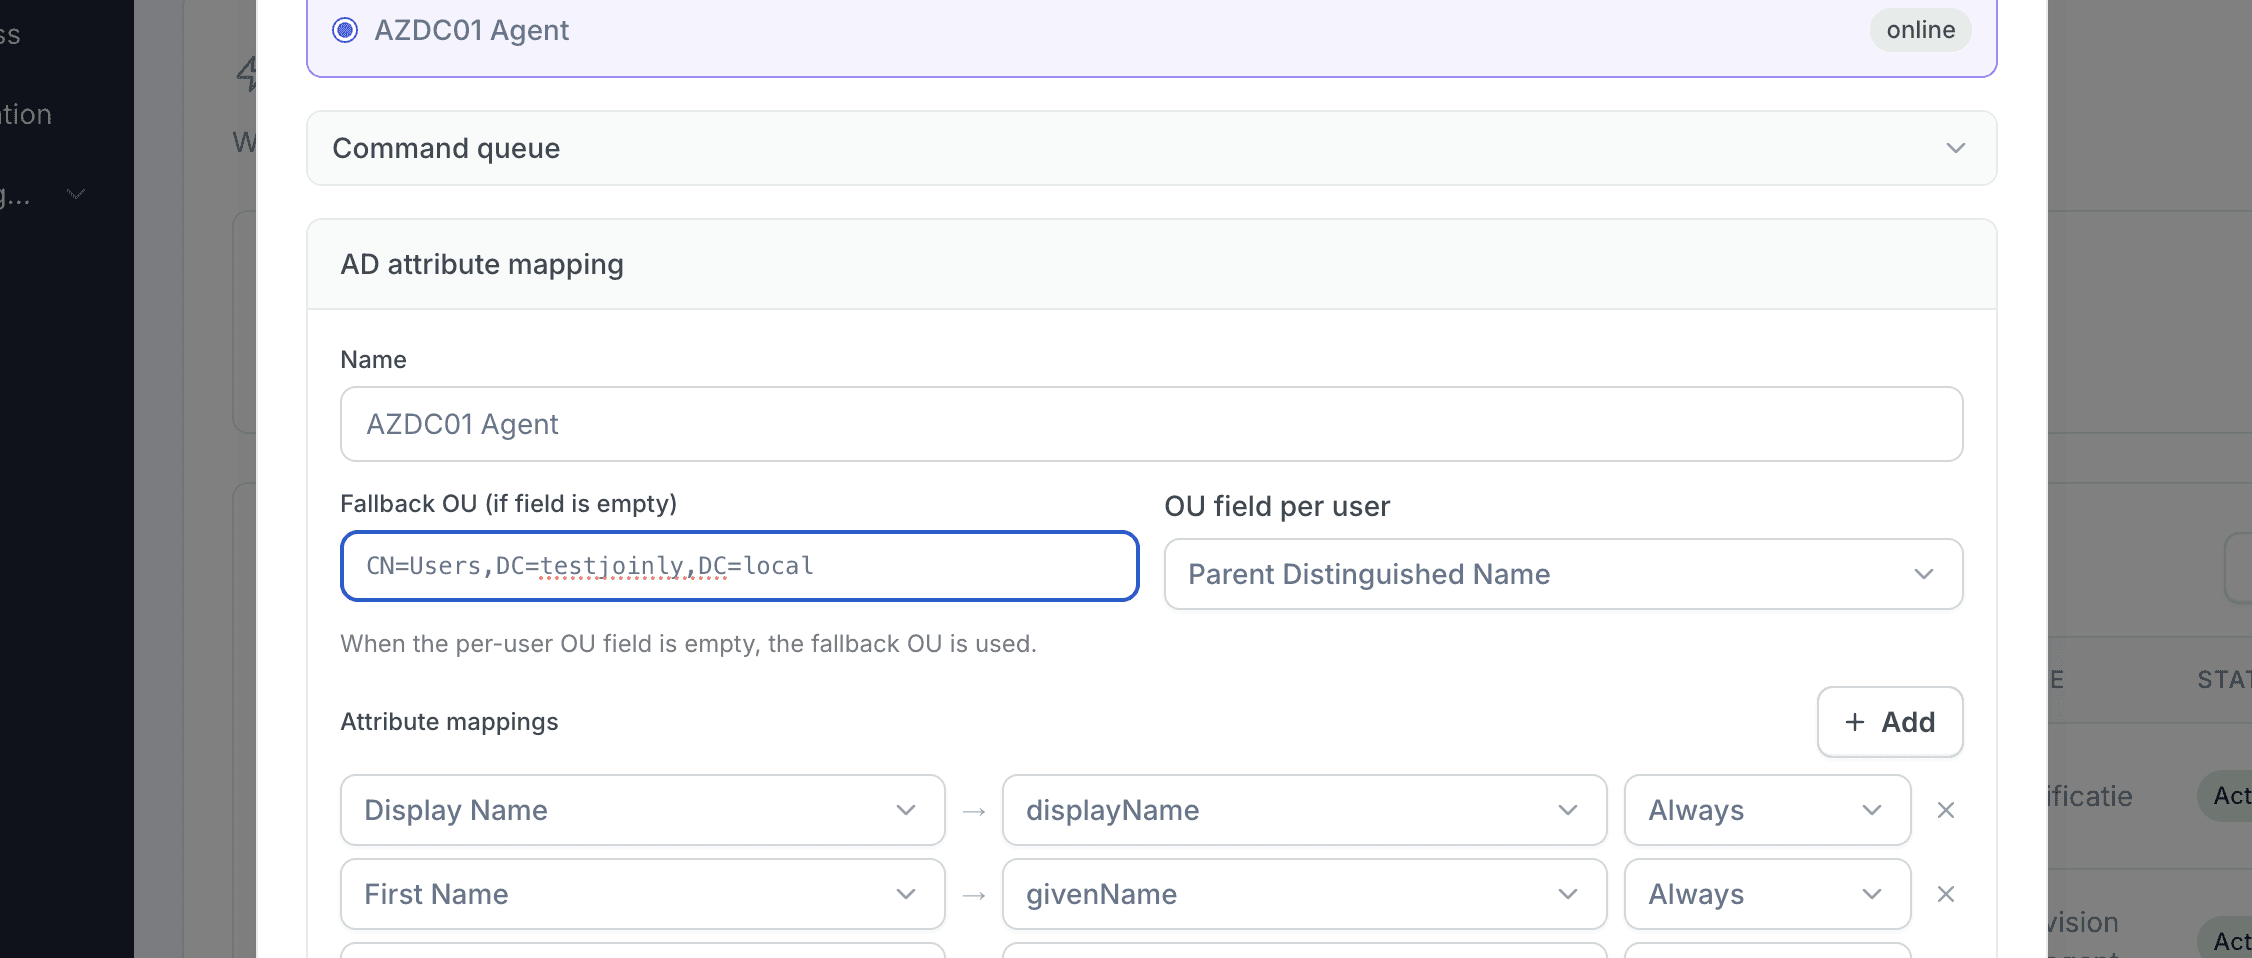
Select the OU and attribute mapping
8. Configure your workflows
Create an onboarding (joiner) and offboarding (leaver) workflow with trigger-based execution, then an Identity updated workflow with a Create/update employee in Active Directory action so every change in Employee Central flows through the agent to AD. Add a threshold workflow that disables the account a set period after the termination date (for example 30 days), optionally moving it to a disabled-users OU.
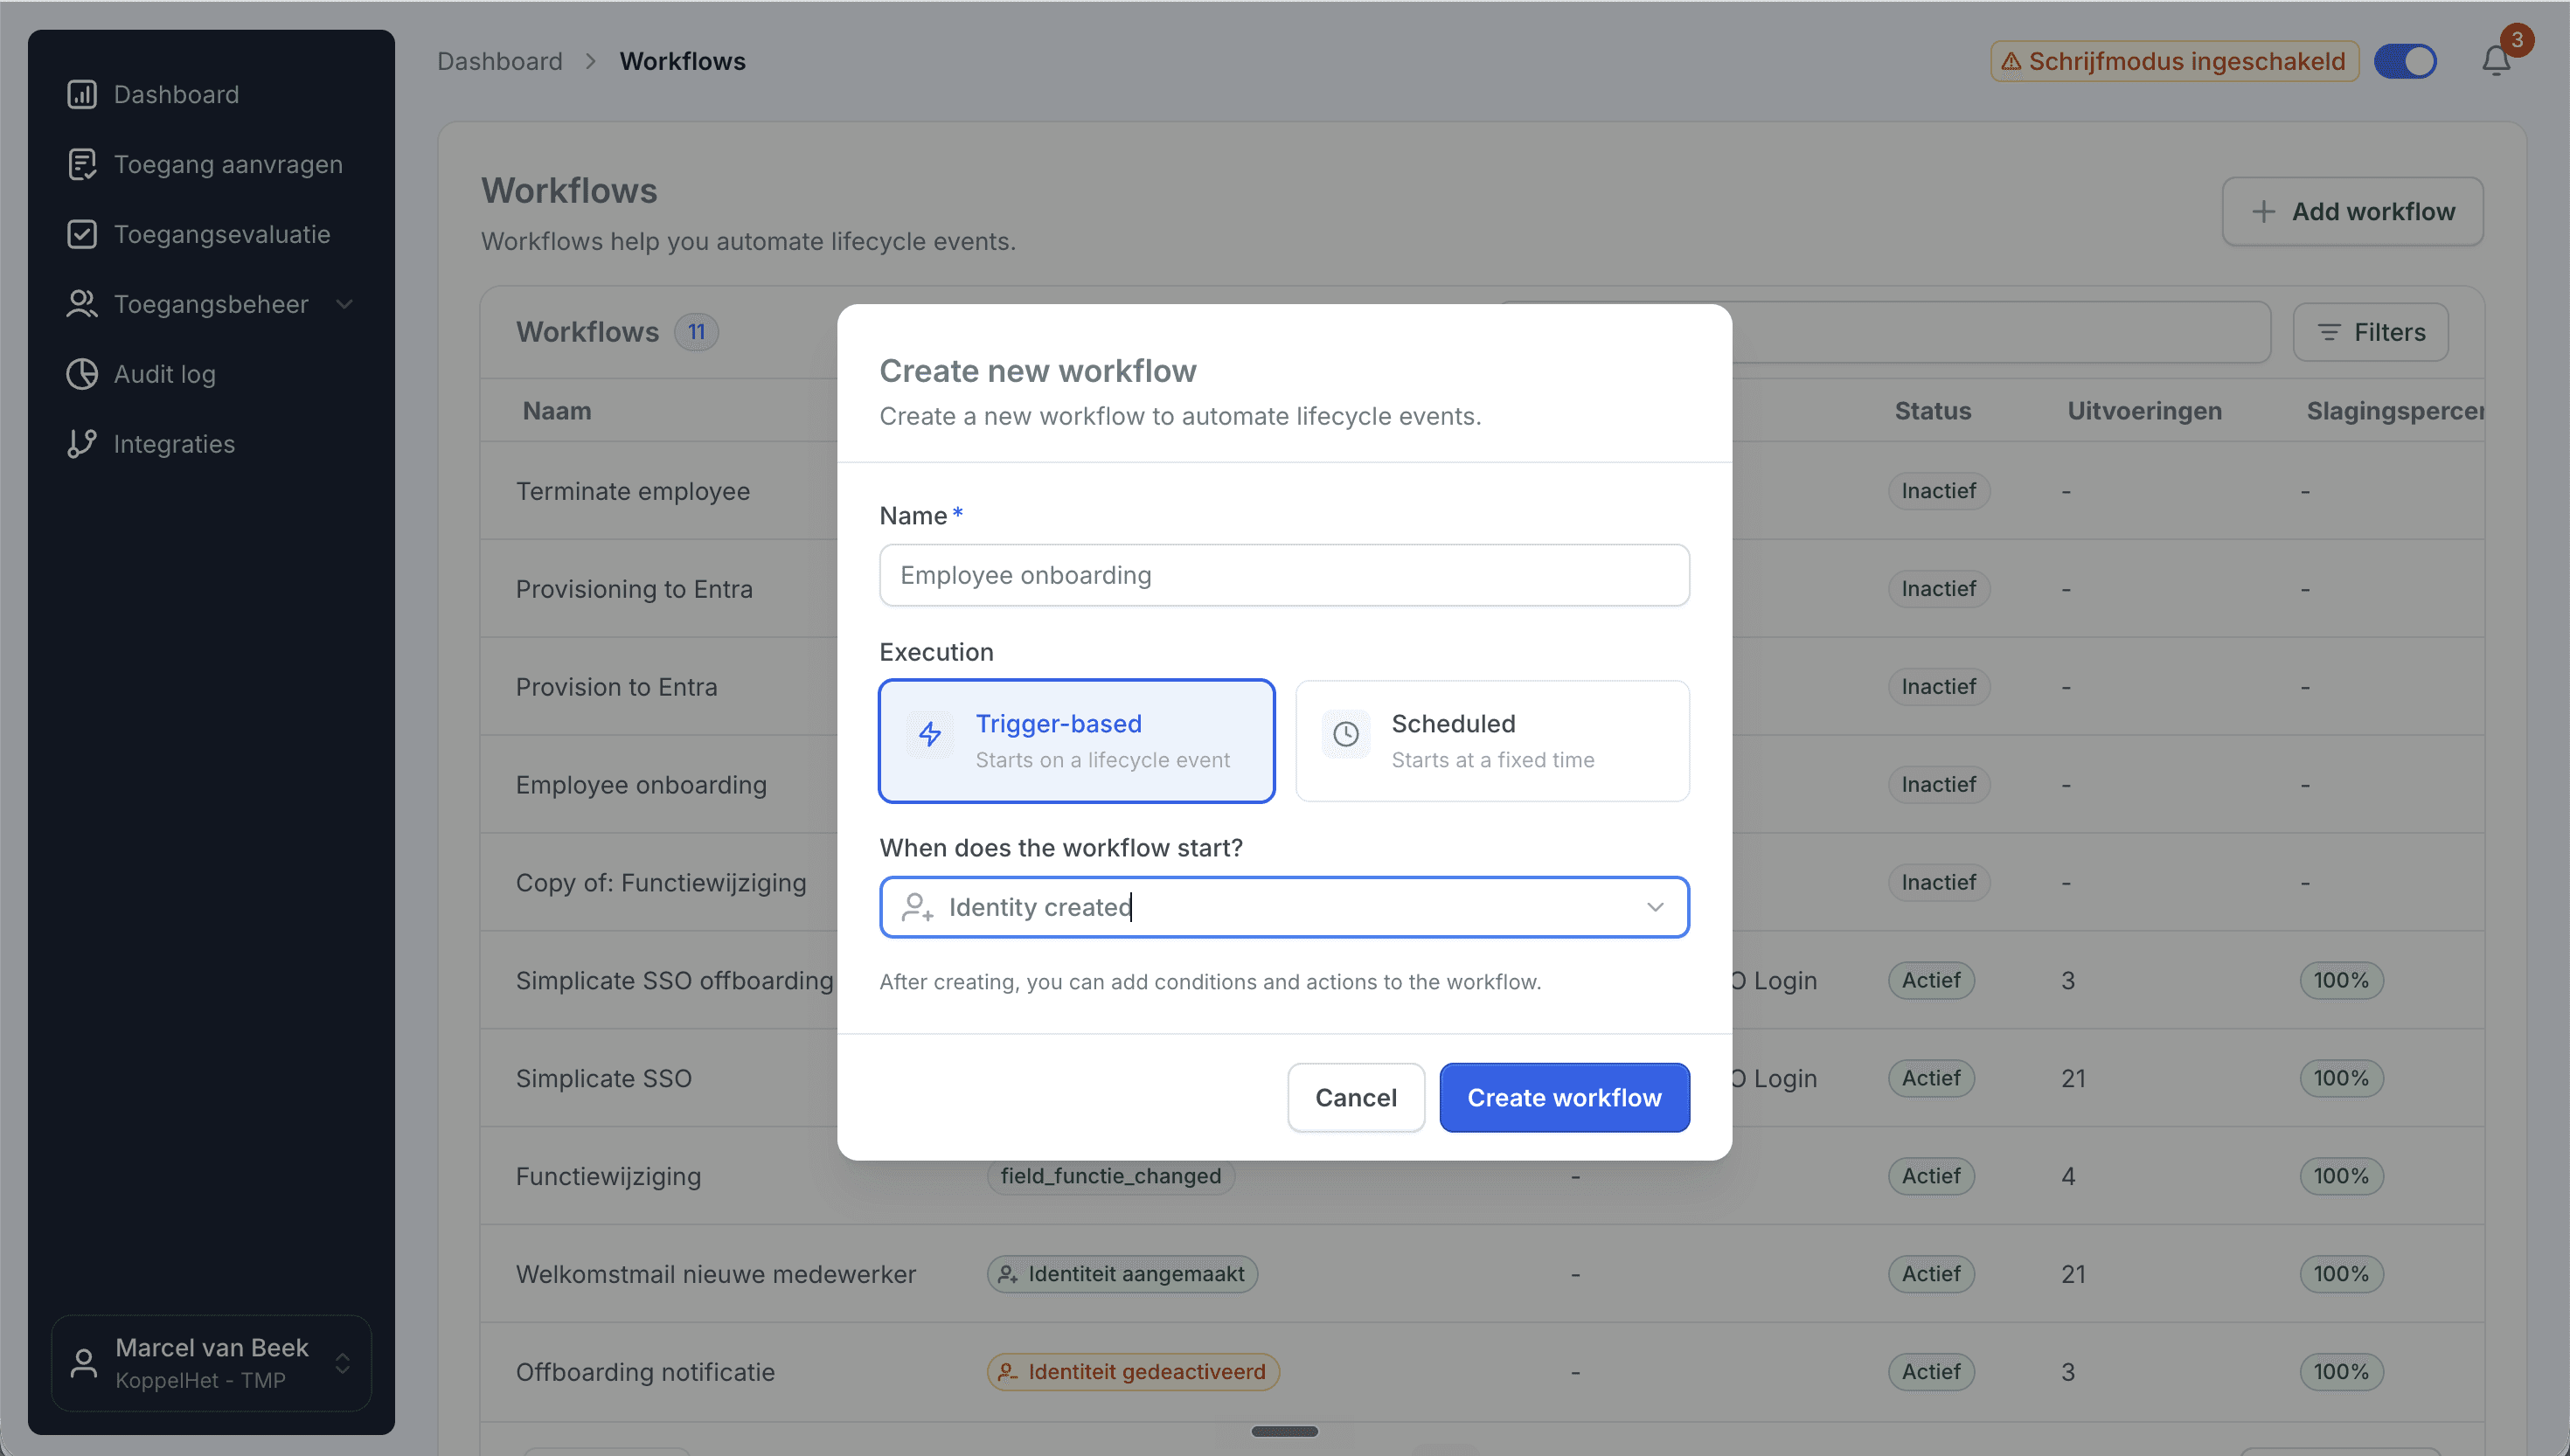
Create a trigger-based onboarding workflow.
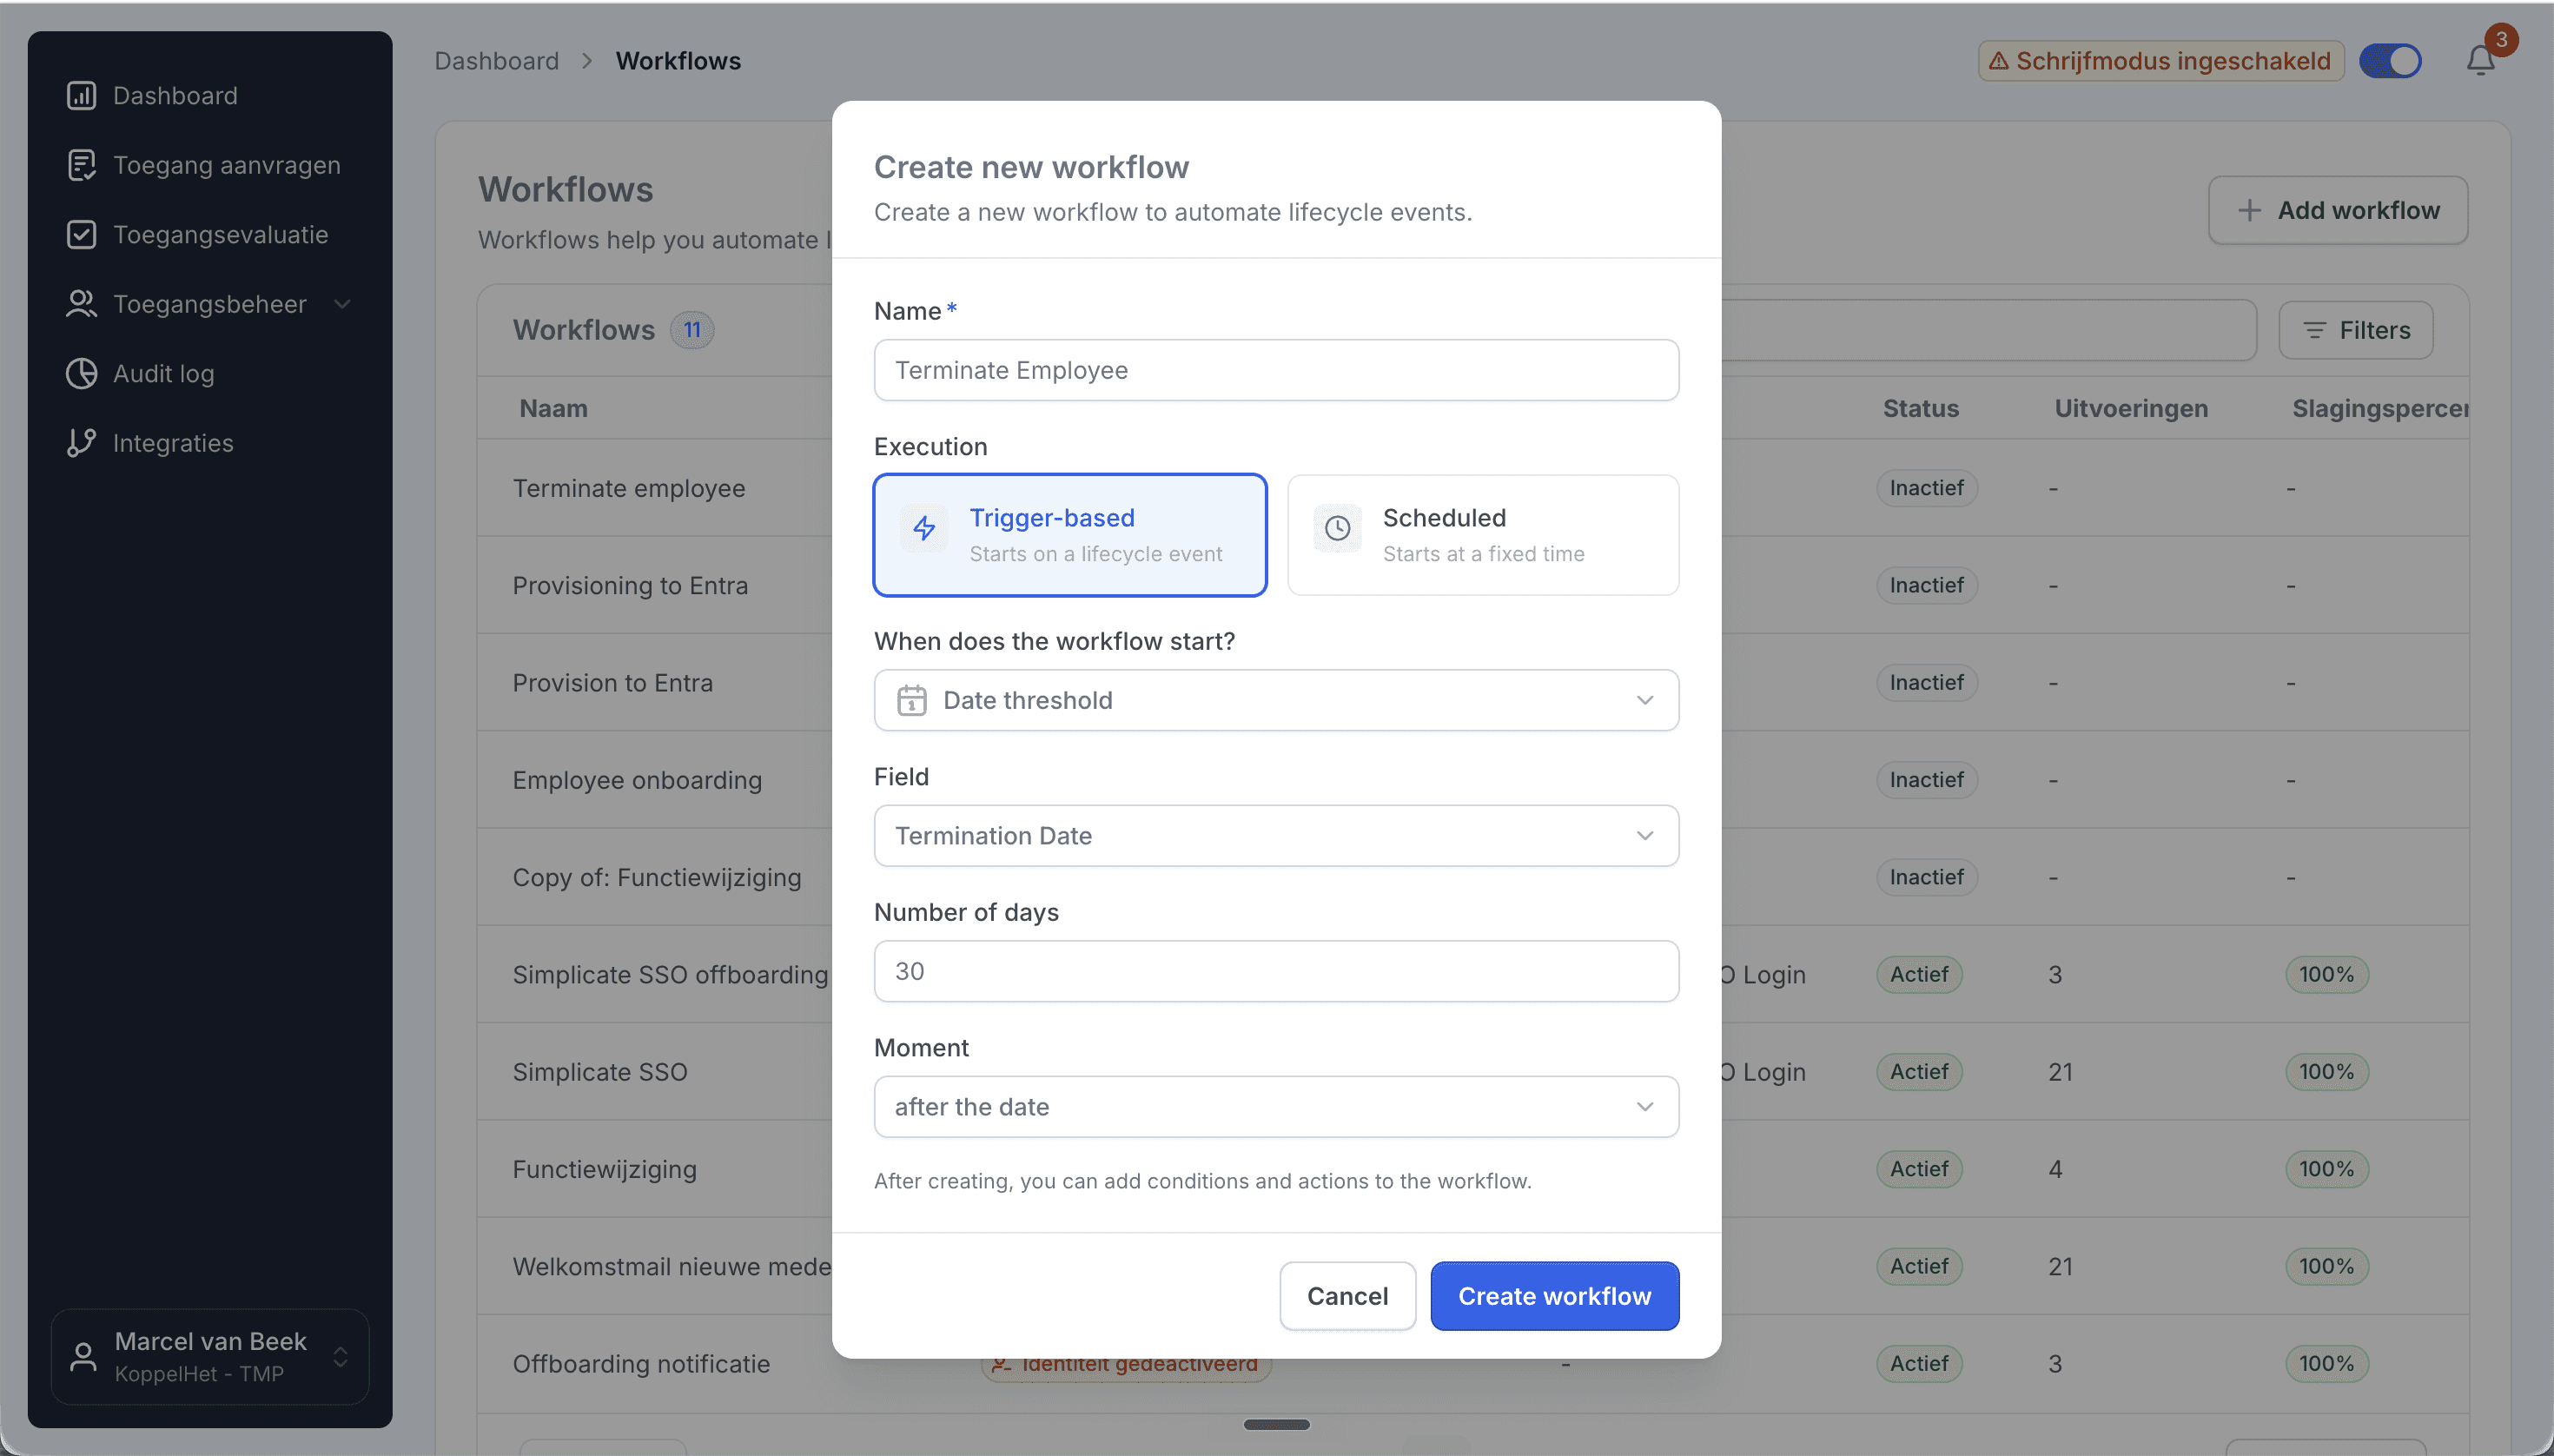
A date-threshold workflow disables accounts a set number of days after termination.
10. Network and firewall requirements
The agent needs outbound HTTPS (443) to the Joinly cloud and a GMSA account with Powershell access to your domain controllers. No inbound firewall rules are required, and no domain controller is exposed to the internet. For high availability you can run the agent on more than one server.
Need cloud Entra ID provisioning as well? See our guide on connecting SAP SuccessFactors to Microsoft Entra ID, or contact support at support@koppelhet.nl.
More than a connector
A standalone SuccessFactors to Active Directory connection is a good start, but identity rarely stops at one target. The same Joinly setup extends to Entra ID for a hybrid environment and to your other systems, managing the complete chain from joiner to leaver with logging and governance built in. You review the exceptions; Joinly maintains the chain.
Request installation support
Frequently asked
Questions about connecting SAP Successfactors to AD On premise
How does Joinly connect SAP SuccessFactors to on-premise Active Directory?
The connection reads HR changes at the source (Employee Central OData API → Joinly AD Agent → Active Directory.) On the directory side the Joinly AD Agent runs inside your own network and makes the change in Active Directory. The agent polls Joinly for work over outbound HTTPS, so there is no inbound firewall rule, no VPN and no published endpoint. What it needs: domain-joined Windows server, outbound HTTPS (443) only.
Which HR events does the SAP SuccessFactors → Active Directory connection handle?
Joiner, mover, leaver (incl. rehire, worker conversion, concurrent employment). Each event runs the workflow you configured for it: a joiner gets an account, groups and licences before the start date, a mover has the access of the old position removed and the new one added, and a leaver is disabled on the termination date.
Which SAP SuccessFactors attributes are synced to Active Directory?
Name, sAMAccountName, UPN, mail, department, job title, manager, cost center, distinguished name / OU, start and end date. The mapping is configurable per field with Liquid templates, so your own naming convention for the user principal name, display name and e-mail address keeps applying.
How often does Joinly sync SAP SuccessFactors with Active Directory?
Frequent sync, multiple times per day. The import schedule is yours to set — hourly, daily or weekly at a fixed time — and every run only processes what changed since the previous one.
Will Joinly overwrite the accounts that already exist in Active Directory?
No. Joinly first imports your existing directory and matches those accounts to the employees from SAP SuccessFactors. Existing accounts are recognised and adopted rather than created twice. Which matching strategy applies — user principal name, e-mail address, employee ID or a person identifier — is a setting.
Can I try this without anything being written?
Yes. Run the import as a dry run and you get an Excel export of exactly what would happen. You can also leave the connection in read-only mode, where Joinly calculates everything but writes nothing, and set thresholds for how many creations, activations and deactivations one run may produce before it is blocked for approval.
Is SAP SuccessFactors a ready-made connector in Joinly?
Yes. SAP SuccessFactors is a ready-made HR connector in Joinly: you enable it, enter the details of your SAP SuccessFactors environment and Joinly reads the employees from there. Nothing has to be developed on either side.
What happens when someone has more than one contract in SAP SuccessFactors?
Joinly recognises that it is one person and decides which employment leads for the account, the manager and the department. You do not get two accounts for the same employee, and when one contract ends the account is only disabled when the last active employment ends.
Do I have to open my firewall for the Joinly AD Agent?
No. The agent initiates every connection itself: it checks in, collects pending commands and reports the result back. Because execution is asynchronous, a workflow waits for the real outcome from Active Directory before the follow-up steps run, so you never get a false confirmation.
Does the SAP SuccessFactors → Active Directory connection support NIS2 and ISO 27001?
ISO 27001, NIS2-ready, GDPR (EU data centre). Every mutation lands in the audit log with its source — HR import, manual, from Entra, by the system or through an API key — and a link to the workflow that caused it. That is the evidence an auditor asks for when they want to know who had access to what, and why.
More on SAP SuccessFactors
Everything Joinly publishes about SAP SuccessFactors: the other installation guide, how the connection compares with Microsoft's own provisioning, what offboarding looks like, and the SCIM route.
See what Joinly can do for your organisation?
Start a free trial today or get in touch for advice on your HR and Microsoft environment.