
Overig · Overig
The architecture of Joinly explained: how everything integrates
Joinly integrates HR systems, Microsoft Entra ID, and applications through a secure and scalable architecture. This article explains how it works, step by step and without technical jargon.
Marcel van Beek · CTO · 6 min read
1. Three layers in the Joinly architecture
Joinly is built from three logical layers that work together:
The source systems (HR)
HR systems such as AFAS, Visma, or Nmbrs provide the employee data.
Joinly retrieves this data via a secure API connector.The Joinly Core (processing layer)
This is where the logic happens. Joinly compares HR data with the current situation in Microsoft Entra ID and determines what needs to change.
This part includes:The lifecycle engine (joiners, movers, leavers)
The mapping engine (translating fields and rules between systems)
The provisioning engine (creating, updating, deactivating accounts)
The target systems (targets)
These are systems where Joinly manages accounts, such as Microsoft Entra ID, Active Directory, Exchange, or SaaS apps via SCIM.
2. HR-driven provisioning as a starting point
Most organisations use HR as the source of truth.
When HR registers a change (for example, a new employee or job change), Joinly detects this and initiates a provisioning flow.
Joinly then determines:
Which accounts need to be created or modified
Which rights and groups are associated with that
Which licences need to be assigned
This logic is stored in the Joinly Core and can be extended per organisation with rules, approvals, or exceptions.
3. Delta API for efficiency
Joinly uses the Delta API from Microsoft Entra ID to retrieve only changes.
Instead of reading all users again every night, Joinly asks:
“What has changed since the last time?”
This makes the system fast, efficient, and scalable, even with thousands of users.
4. Secured communication
All communication takes place via secure HTTPS connections with OAuth 2.0 authentication.
Tokens are stored encrypted and renewed periodically.
No system gets more access than strictly necessary (least privilege).
When connecting to on-premises environments (such as Active Directory), Joinly uses:
A hybrid connector or Azure Function in the customer environment
Only outgoing connections, so no open ports from outside
5. Expandable via connectors and APIs
Joinly is built modularly.
New connections are added as connectors:
HR connectors (AFAS, Visma, Youforce, Personio, etc.)
Target connectors (Microsoft Entra, AD, HubSpot, Exact, Topdesk, etc.)
Each connector uses the same underlying provisioning framework, ensuring expansions remain consistent.
6. Summary
The architecture of Joinly is easy to visualize:
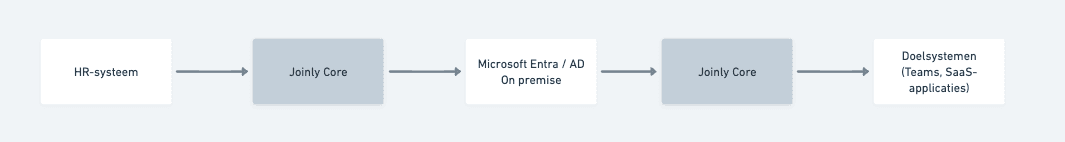
HR determines what changes
Joinly Core translates and automates
Changes are forwarded to Microsoft Entra ID/AD On Premise
Users are forwarded from Microsoft Entra to Target systems and Microsoft Applications such as Teams, SharePoint, and Exchange with the correct rights
Conclusion
The power of Joinly lies in simplicity: HR provides the data, Joinly processes the logic, and via secure APIs all systems are kept up-to-date.
Whether that is in the cloud or on-premises, the architecture remains the same: secure, modular, and scalable.
Explore more blogs

Segregation of Duties (SoD): wat het is en hoe je het afdwingt
Wat is segregation of duties (functiescheiding)? Uitleg, voorbeelden en waarom het vaak misgaat. Plus hoe je SoD-conflicten automatisch tegenhoudt.
Marcel van Beek · 4 min read

How do you apply AGDLP in a hybrid Entra/AD environment? (And why you shouldn't want to anymore)
Short answer: preferably not. AGDLP (Accounts → Global groups → Domain Local groups → Permissions) is a concept from the era of manual management. The entire nesting construction exists for one reason: to allow a human to assign permissions with as few mouse clicks as possible. As soon as an agent assigns group memberships directly based on HR data, this reason disappears and only the complexity remains. Moreover, in a hybrid environment, this complexity actively works against you, because Entra ID completely ignores nesting for licences and app assignment. In this article, you can read how AGDLP works and why it was once smart, where it breaks down in a hybrid environment, and what the modern alternative looks like: direct memberships, managed by automation.
Marcel van Beek · 5 min read

How do I set up role-based access control (RBAC) and least privilege for a municipality?
Start with the roles in your HR system and map them to roles, not to individual permissions per person. Group each role with precisely the access required for the job, adhering to the principle of least privilege. Manage these roles centrally and let an orchestration layer automatically assign and revoke them. This keeps access predictable, limited and demonstrable.
Mike Fraanje · 4 min read
See what Joinly can do for your organisation?
Start a free trial today or get in touch for advice on your HR and Microsoft environment.